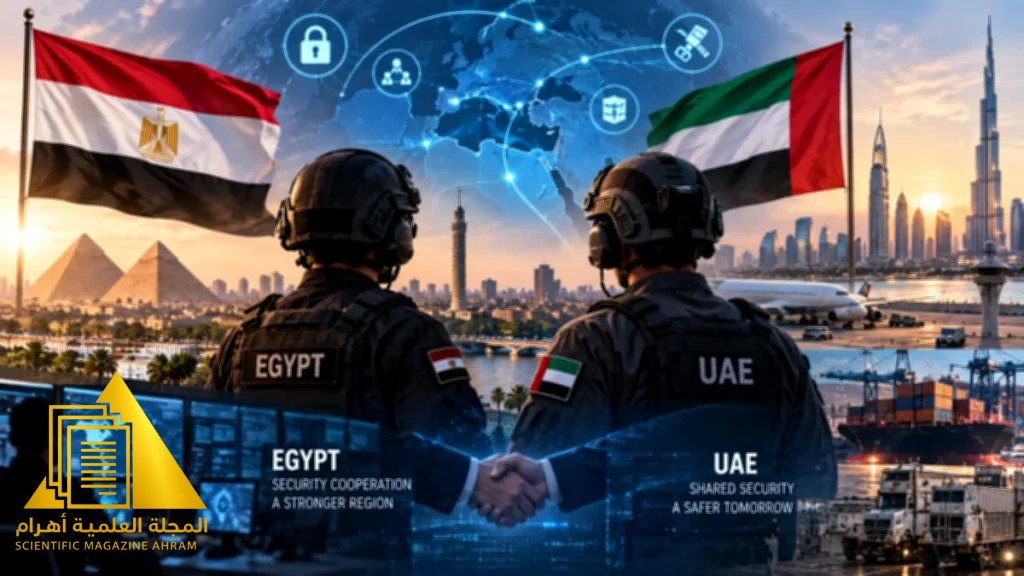

Two countries may possess strong security institutions, advanced expertise, and modern technologies, yet still lose precious time when a threat crosses a border. The problem here is not necessarily a lack of capability on either side; rather, it may simply be that operational cooperation begins only after a crisis emerges, instead of being designed as a core part of preparedness before an incident occurs.
This gap deserves greater attention in a world where crime, money, data, cyberattacks, and supply chain disruptions move across borders at speeds that do not wait for traditional institutional procedures.
From my experience in security, operations, and risk management, I believe the question is no longer whether institutions can cooperate—in many cases, they already can. The more useful question is: How long does it take for cooperation to move from a mere contact between two institutions to actionable intelligence, and then to a decision made while it can still change the outcome?
Security Interoperability: From Communication to Action
This is where the importance of security interoperability comes in. This does not mean that different institutions must use the same systems, nor that countries must unify their laws and procedures. Every country has its own sovereignty, legislation, and institutional structure.
The goal is not to eliminate these differences, but to make them compatible and able to work together when needed.
A cross-border threat does not pause to ask which organizational structure will handle it. This is why genuine cooperation begins before it is needed.
A relationship that relies solely on individuals knowing one another may work exceptionally well in a specific instance, but it remains vulnerable to changes in personnel, responsibilities, and structures.
An institutional relationship, however, endures because it predetermines who contacts whom, what information can be shared, what level of trust is required, what path urgent information takes, and who holds the authority to escalate when time becomes a decisive factor.
This is particularly important in the relationship between Egypt and the UAE.
Egypt possesses significant human, geographical, and institutional scale, along with extensive experience operating within a complex security environment. Meanwhile, the UAE operates in an environment deeply connected to the world through aviation, ports, financial services, logistics, and digital government.
The value does not lie in claiming that one country possesses what the other lacks, but in the fact that differing operational environments can generate shared knowledge that is broader than the experience of either country alone.
When Crime Moves Faster Than Institutions
Imagine a fraud network where contact with the victim begins in one country, funds move through an account in a second country, its digital infrastructure is hosted in a third, and it is managed by individuals from somewhere else.
Each entity may hold a correct piece of the picture, but no one sees the full picture at first.
The problem is not just the absence of information, but the time required for these pieces to meet.
From this, a useful metric for preparedness can be proposed: international cooperation time.
How long does it take for critical information to travel from the agency that discovered it to the agency capable of taking action? How much of that time is genuinely necessary to uphold the law, privacy, procedural integrity, and evidence handling, and how much is merely friction that can be avoided through poor institutional design?
Speed Does Not Mean Overstepping the Law
Speed should not be confused with bypassing the law.
Legal procedure is not an obstacle to security; it is part of what grants a security measure its legitimacy and protects evidence, rights, and decisions.
However, there is a difference between the time required for a genuinely authorized legal process and the time wasted because information reached the wrong desk, arrived in an unusable format, or lacked clear instructions on the required action.
Therefore, institutions that cooperate frequently need a shared operational language.
I do not mean a spoken language, but a shared way to describe a situation: What do we know? What do we suspect? What do we not yet know? What is our level of confidence in the information? What action is required? And how time-sensitive is the matter?
Under pressure, these distinctions become critical.
A phrase like "we have a potential threat" can carry different meanings for two institutions, whereas information becomes far more useful when it includes the confidence level, the source status, what has been verified, what remains unconfirmed, and what should be done within a specific timeframe.
Testing the Journey of Information Instead of Just Exchange
This leads to another practical proposal: rather than merely testing the ability of agencies to exchange information, we should test the journey of the information itself.
A joint exercise might begin with a weak signal inside one institution, evolve as the scenario requires another national agency, and then extend to a partner institution in a second country.
The goal is not to prove that everyone has the right phone numbers, but to measure time, accuracy, and friction points.
Where did the information slow down? Did the first employee realize it deserved escalation? Did it reach someone with the authority to act? Did the receiving party understand what was required? Was the context sufficient to take action? And did the information retain its meaning as it moved across systems and institutions?
Exercises of this kind turn good relations into a capability that can be measured and improved.
AI Accelerates Discovery, But Does Not Solve the Operational Problem
Artificial intelligence adds another layer to this issue.
Modern systems can analyze vast amounts of data and uncover links among variables, events, or patterns that humans struggle to detect at the same speed.
A signal in Egypt may become more meaningful when linked to data in the UAE, or vice versa.
Yet technology alone does not solve the challenge of interoperability. An algorithm may discover a relationship within seconds, while institutions need hours or days to determine what they can legally and operationally do with it.
Therefore, investing in algorithms without investing in the decision-making pipeline can produce insights faster than an organization can use them.
It must also remain clear that statistical correlation is not proof of guilt. Artificial intelligence can point to a pattern worth investigating, but it should not turn computational suspicion into a verdict.
Human expertise, verification, and the law remain essential elements.
Collaboration Does Not Mean Opening a Single Database to Everyone
Furthermore, modern security collaboration does not need a giant database that everyone has the right to access; this can create major security, legal, and privacy risks.
The better model is to set clear rules that define what is shared, when, with whom, for what purpose, and under what protection.
Trust between institutions does not mean removing boundaries, but making those boundaries understood and actionable.
Security Collaboration Goes Beyond Crime
The same logic goes beyond crime.
It applies to cyber incidents, where an attack detected in one institution may be part of a broader campaign. It applies to aviation, ports, energy, and supply chains, where a disruption in one place can spread to sectors that were not party to the original event.
Modern threats move horizontally across sectors and borders, while institutions necessarily operate within vertical structures of authority and responsibility.
The challenge is not to dismantle these structures, but to build bridges between them that operate at the speed the threat demands.
From Crisis Coordination to Pre-Crisis Readiness
From this perspective, the relationship between Cairo and Abu Dhabi can be viewed as an opportunity to develop a more advanced model for Arab security cooperation—a model that does not wait for a case or crisis to begin coordination, but practices beforehand how information, decisions, and responsibility pass between institutions.
The real achievement is not simply announcing that cooperation exists, as it already exists in various forms.
The next step is to make cooperation faster, testable, and more sustainable even as people, technologies, and conditions change.
In security, strong relationships are not enough if knowing how to use them is kept only in the memory of a limited number of individuals.
Relationships must turn into institutional memory: clear procedures, exercises, channels, and standards that newcomers can use.
The Real Test: Who Outpaces Whom?
Threats have become skilled at finding gaps: between systems, agencies, jurisdictions, and countries.
Every minute lost determining who should act can turn into space for the threat to move.
Therefore, Arab security needs more than extra information; it needs a stronger ability to deliver the right information to the right place, in an understandable format, and at the moment when a decision can still change the outcome.
Information can cross a border in a second, and so can a threat. The real test is whether the bridges between our institutions can move faster than the gaps the adversary tries to exploit.
Abdullah Saeed Al Habsi
Writer and researcher specializing in security, heritage, risk management, and operations rooms.

Latest video
تابع معنا تحليل قراءة الصحف اليومية مع الكاتب الصحفي Hany Sallam عبر